Enterprise · Identity governance & security · Live multi-tenant platform · formerly WonderAgent
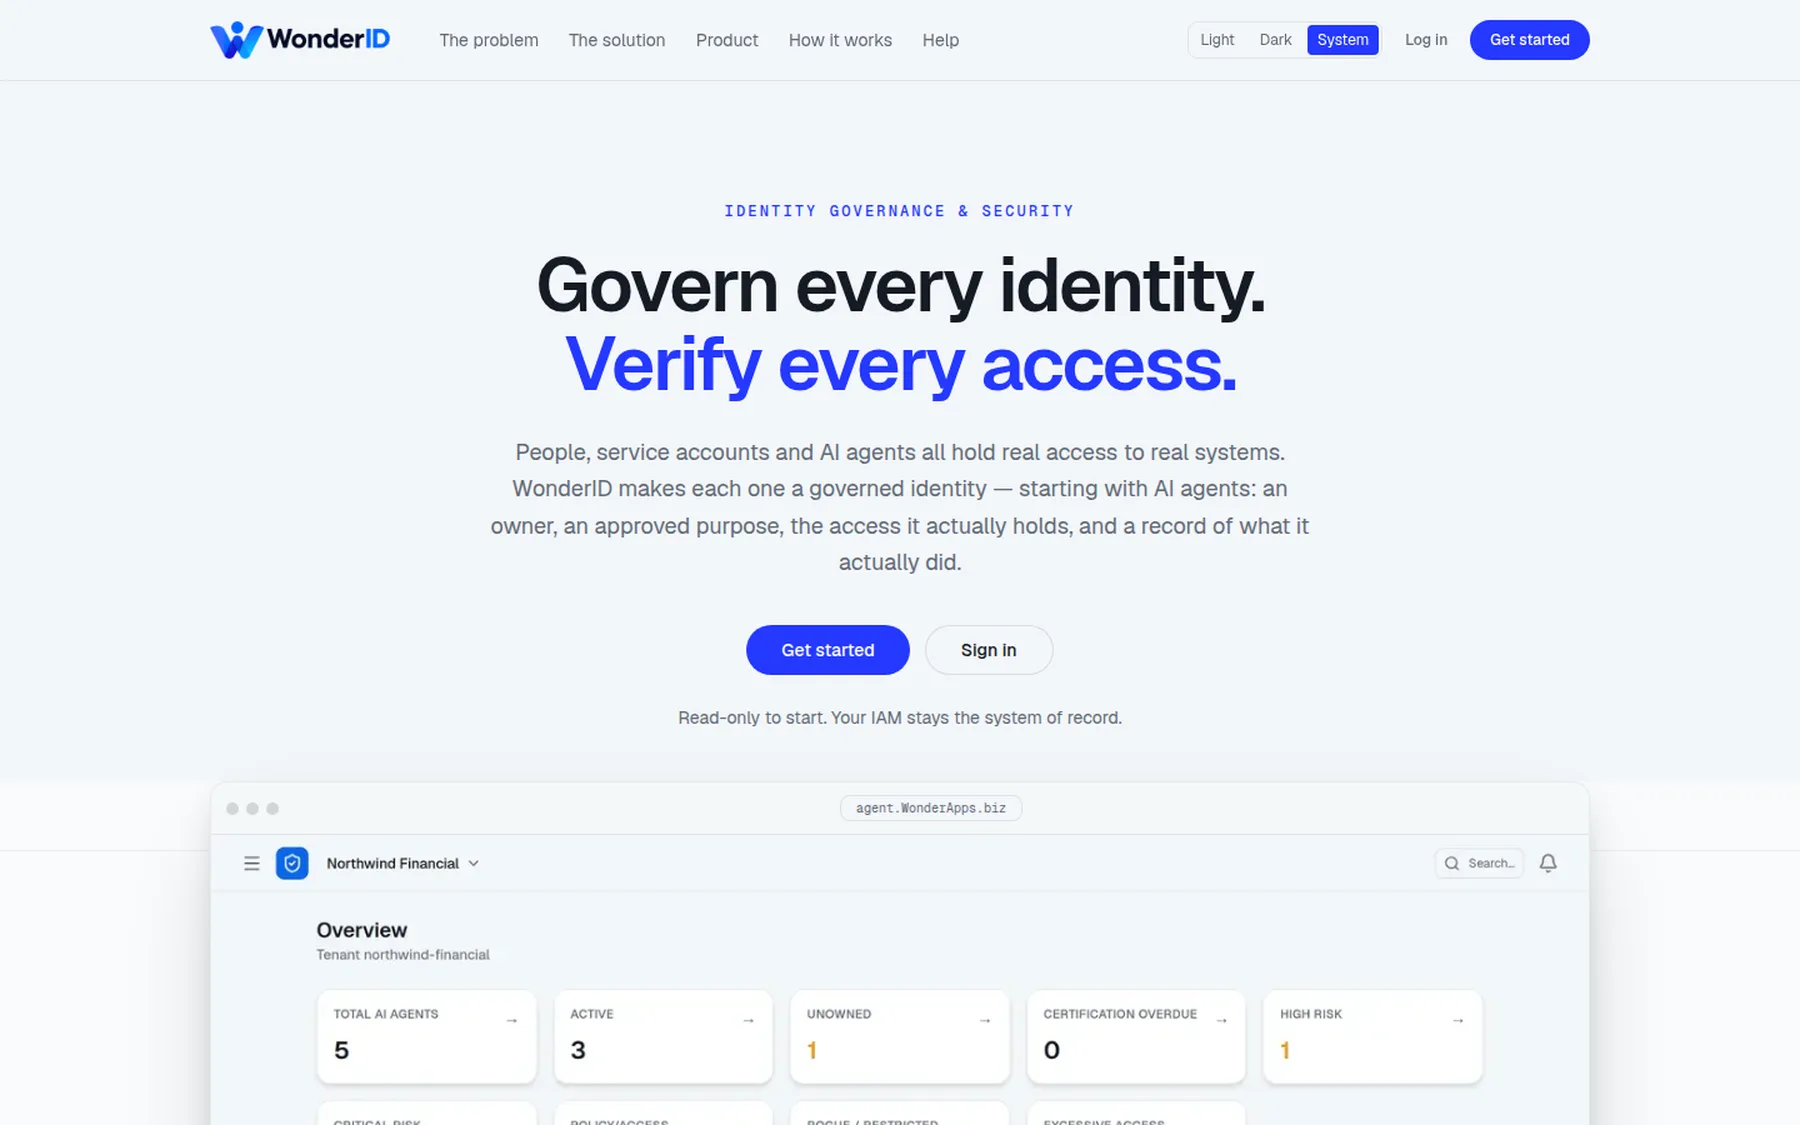
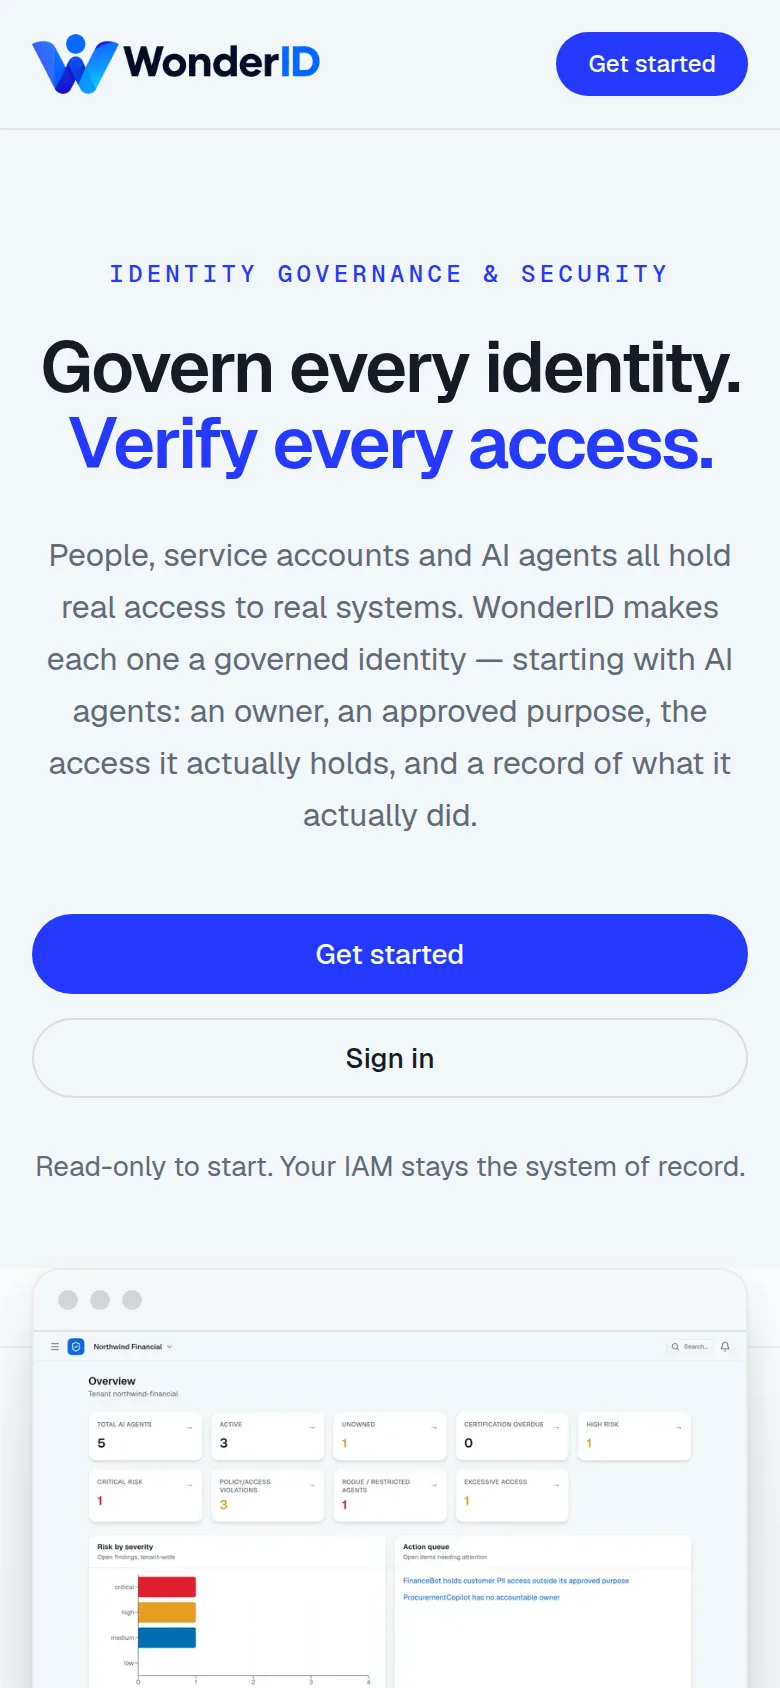
Govern every identity. Verify every access.
People, service accounts and AI agents all hold real access to real systems. WonderID makes each one a governed identity — starting with AI agents, where it compares what an agent SHOULD do, CAN do and DID, and raises an evidence-backed finding the moment they disagree. Read-only to start; your IAM stays the system of record.
- Platform
- Web · responsive · vendor platform-admin console
- AI
- Advisory summaries only — OpenAI / Gemini, platform or BYOK
- Data
- Supabase PostgreSQL, tenant_id + RLS on every table
- Pricing
- Pilot · Enterprise (packaging with design partners)
The problem
AI agents got production access. Nobody gave them an identity.
An agent is provisioned like a service account, inherits access like a person, and acts continuously like neither. Most exist as untracked service accounts — alongside the people and machines no one has reconciled either.
- 1
No owner
Provisioned as SVC_FINANCEBOT_PRD by someone who has since changed teams. No business owner, no technical owner, nobody to approve a change.
- 2
Purpose that no control can read
The agent's approved scope lives in a ticket, a design doc or someone's memory — never anywhere a control can evaluate.
- 3
Access far beyond purpose
Nested groups, OAuth scopes and tool permissions add up to reach that nobody has computed, let alone certified.
- 4
Behaviour disconnected from identity
Runtime logs sit in an observability tool keyed by service name, cut off from the entitlement and approval that allowed the action.
The product
SHOULD. CAN. DID. — then every identity around it.
Agent governance stays at its core; the same deterministic engine now extends to a unified identity directory, application onboarding and self-service access — across the IAM platforms a customer already runs (Saviynt, Okta, Entra, custom IAM and MCP runtimes map into one canonical model).
01
AI agent governance
Every agent gets an owner, a purpose contract and a lifecycle state. Its approved purpose (SHOULD), effective access computed from real entitlements, roles, groups and OAuth scopes (CAN), and observed runtime behaviour (DID) are compared continuously; any divergence is a finding with evidence.
02
One directory for every identity
Humans, external users, service accounts, applications, workloads, APIs and AI agents in one tenant-scoped directory — fed by authoritative sources through a validate, correlate, stage and apply reconciliation pipeline, with joiner, mover and leaver lifecycle.
03
Applications, onboarded properly
An application catalog that surfaces unrecognised apps, onboarding that validates, simulates and needs a four-eyes approval before it goes live, and an account inventory that flags orphaned and dormant accounts. AI can draft an onboarding proposal from an OpenAPI spec; a person approves it.
04
Self-service access, real approvals
A request catalog with per-item policies, multi-stage approval chains that forbid self-approval, and access packages that work the same for people and agents.
05
Risk, certification & evidence
Deterministic scoring — never an LLM guess — for excessive access, unauthorised actions, sensitive-data violations and behavioural deviation. Certification campaigns produce auditor-ready evidence packs.
How it works
From signal to outcome.
Step 1
Connect
Import identities, applications and access from existing IAM and authoritative sources, plus runtime events from MCP or REST. Connectors declare capabilities explicitly; read-only means read-only.
Step 2
Declare purpose
Name an owner, approved applications, approved data classes and approved actions. That contract becomes SHOULD.
Step 3
Compare continuously
Purpose, effective access and observed behaviour are evaluated by explicit rules. Findings carry the evidence that produced them.
Step 4
Remediate with a human
Every recommended revocation waits for a human to confirm, is recorded against the finding, and is re-evaluated once access changes.
Product tour
Desktop and mobile, one product.
Captured from the deployed product. Some views show demonstration data.
The product site — every identity governed, starting with AI agents
The same, on a phone
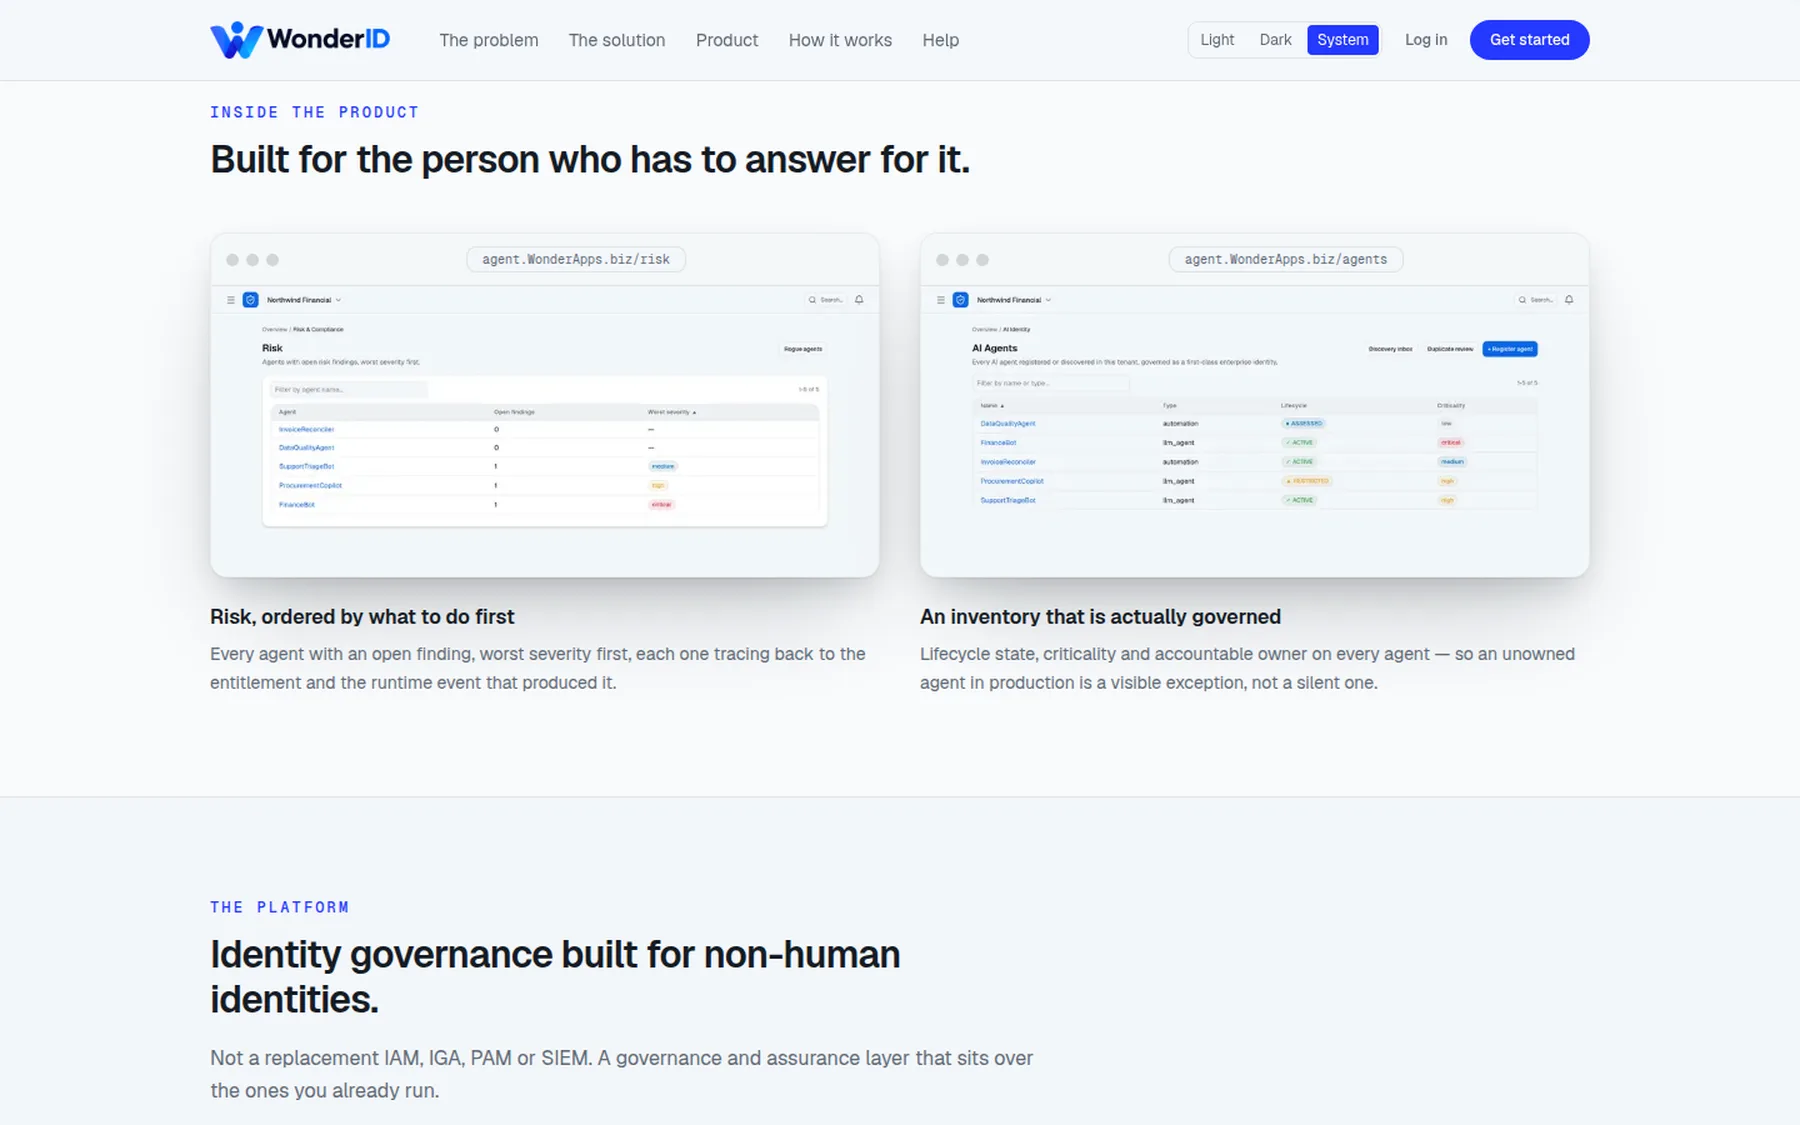
Risk ordered by what to do first; an agent inventory that is actually governed
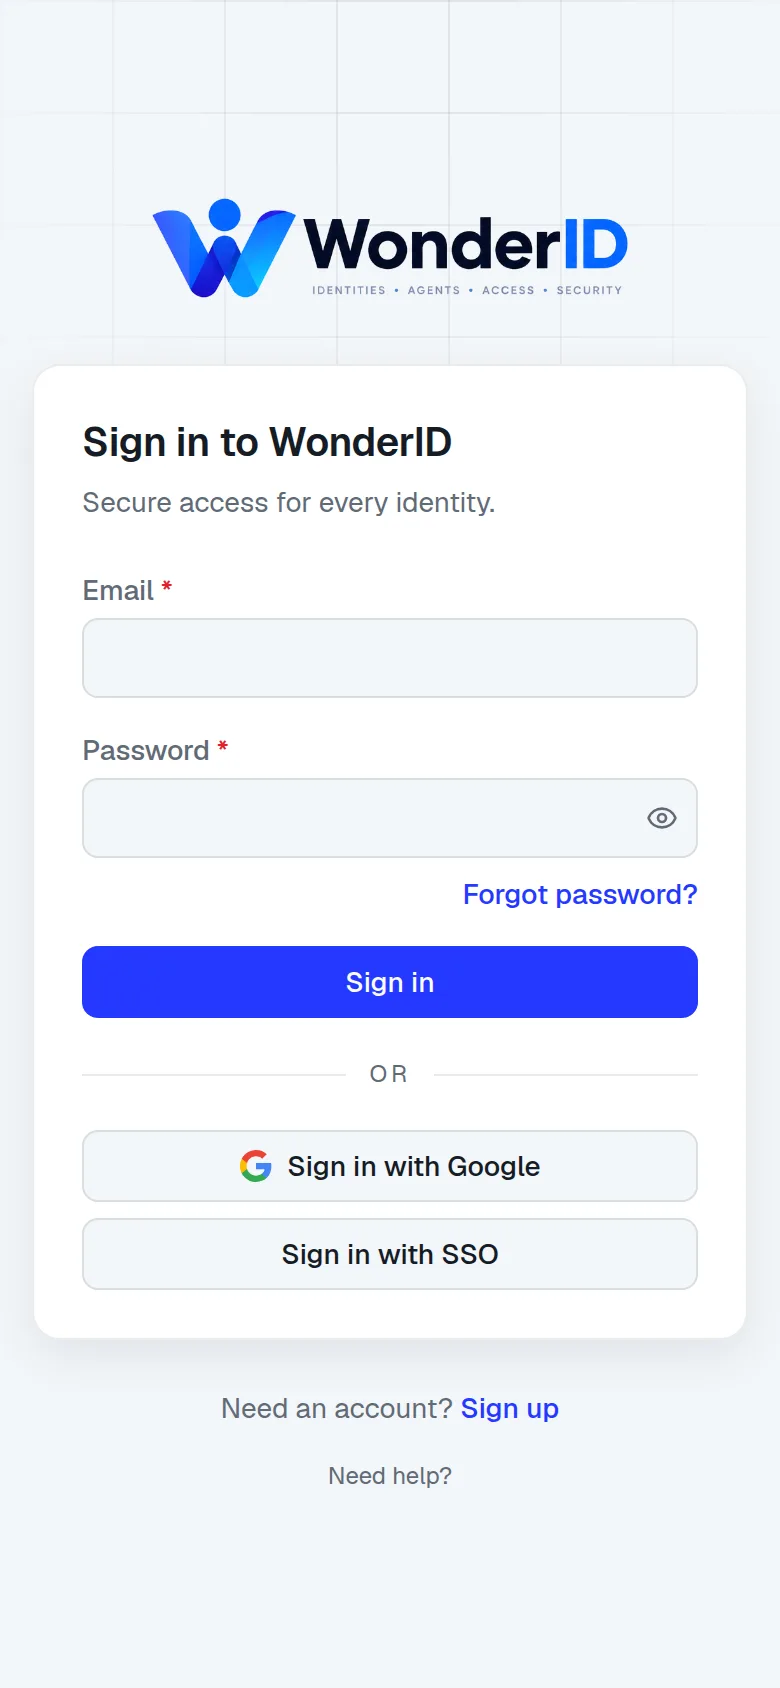
Sign in with email, Google or enterprise SSO
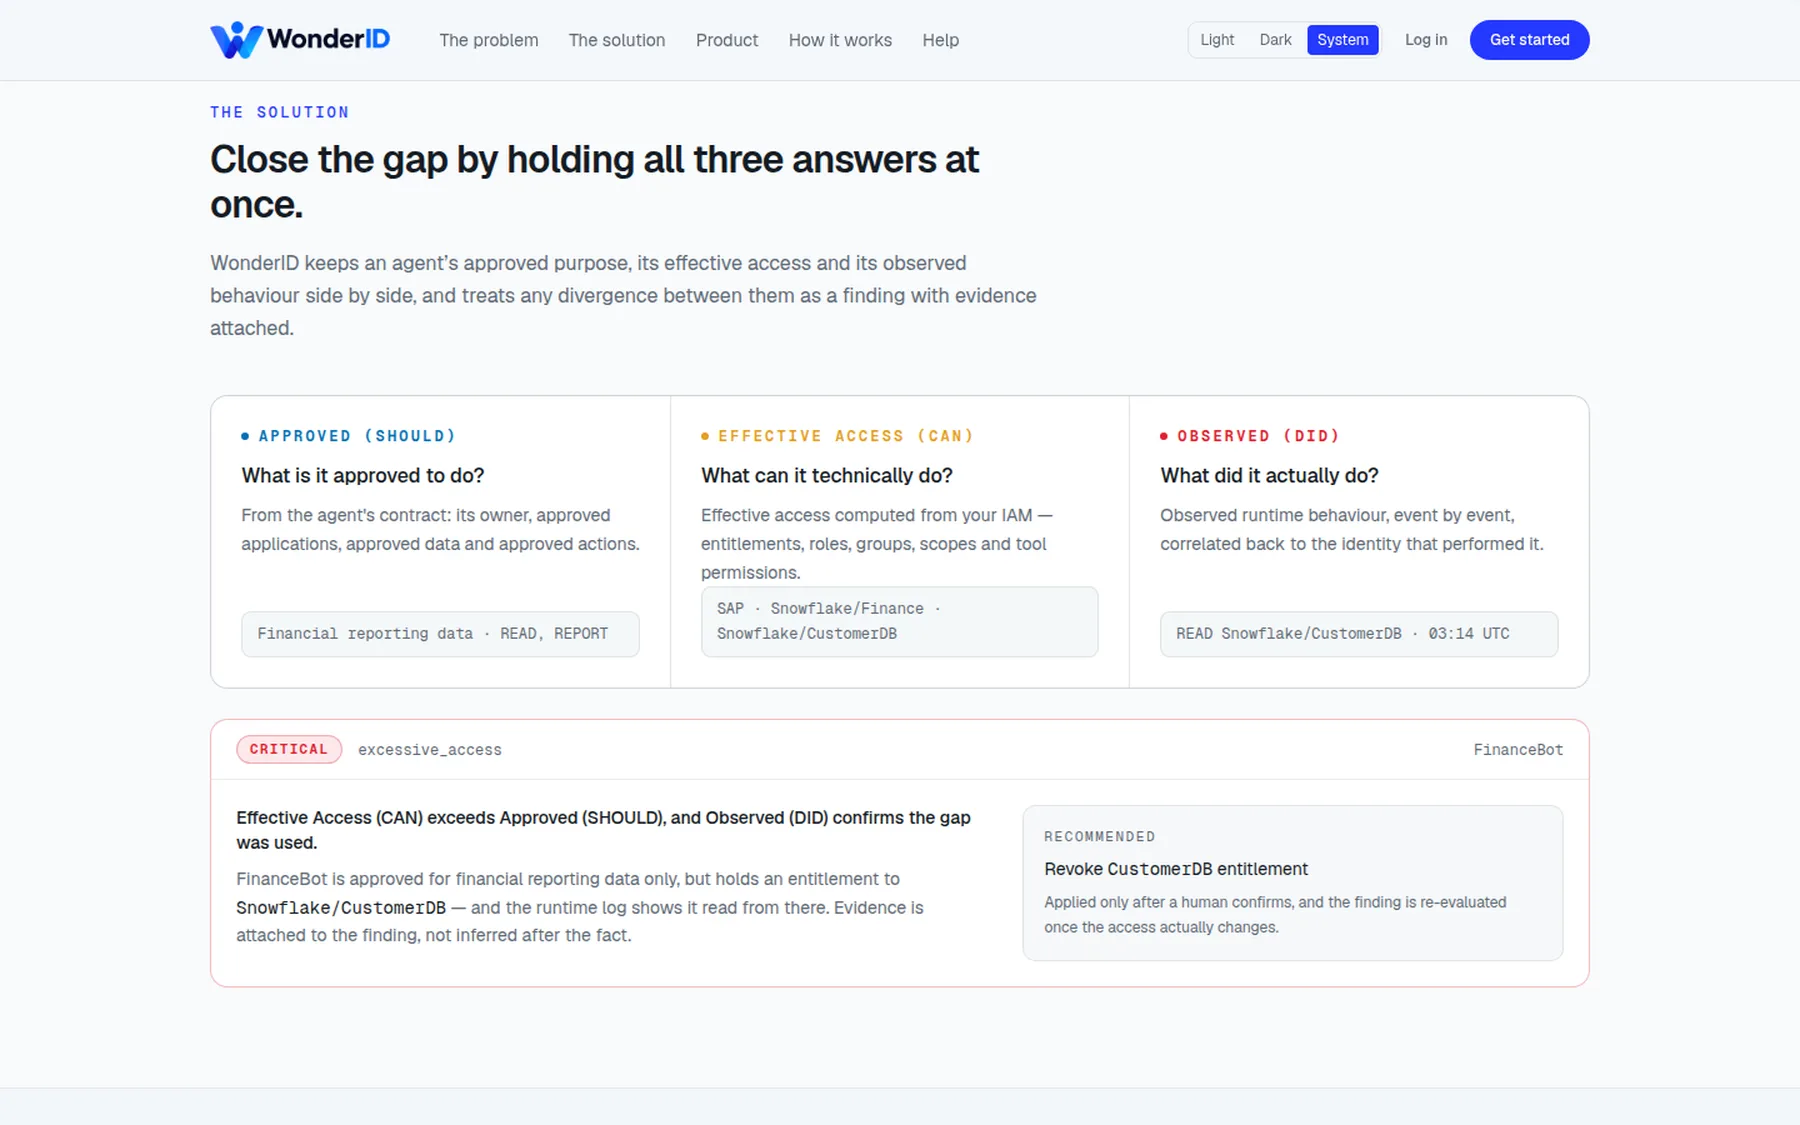
SHOULD · CAN · DID — a critical finding, with the evidence attached
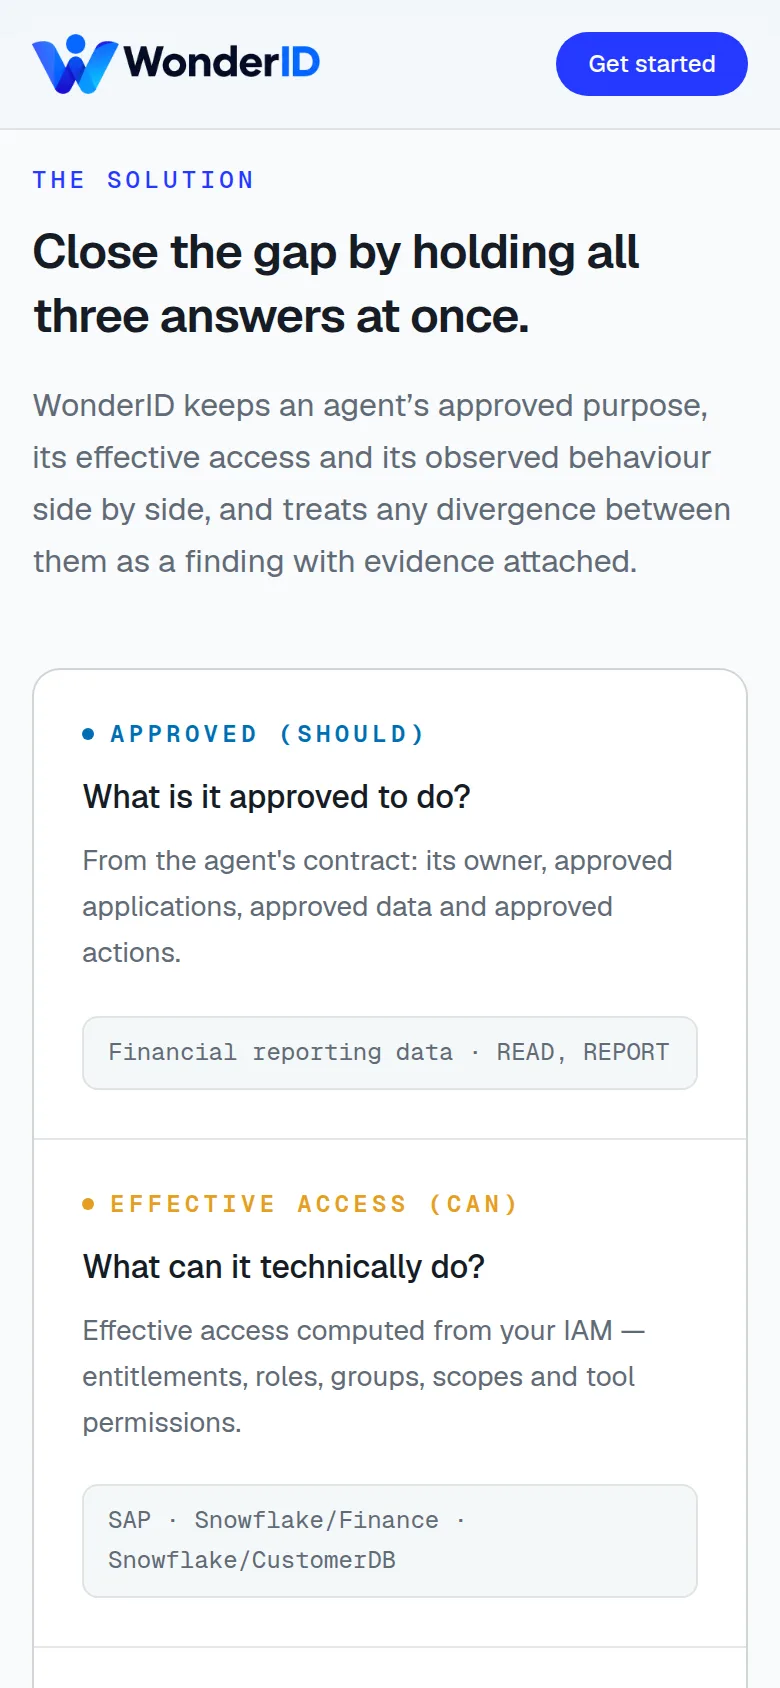
The governance model, on mobile
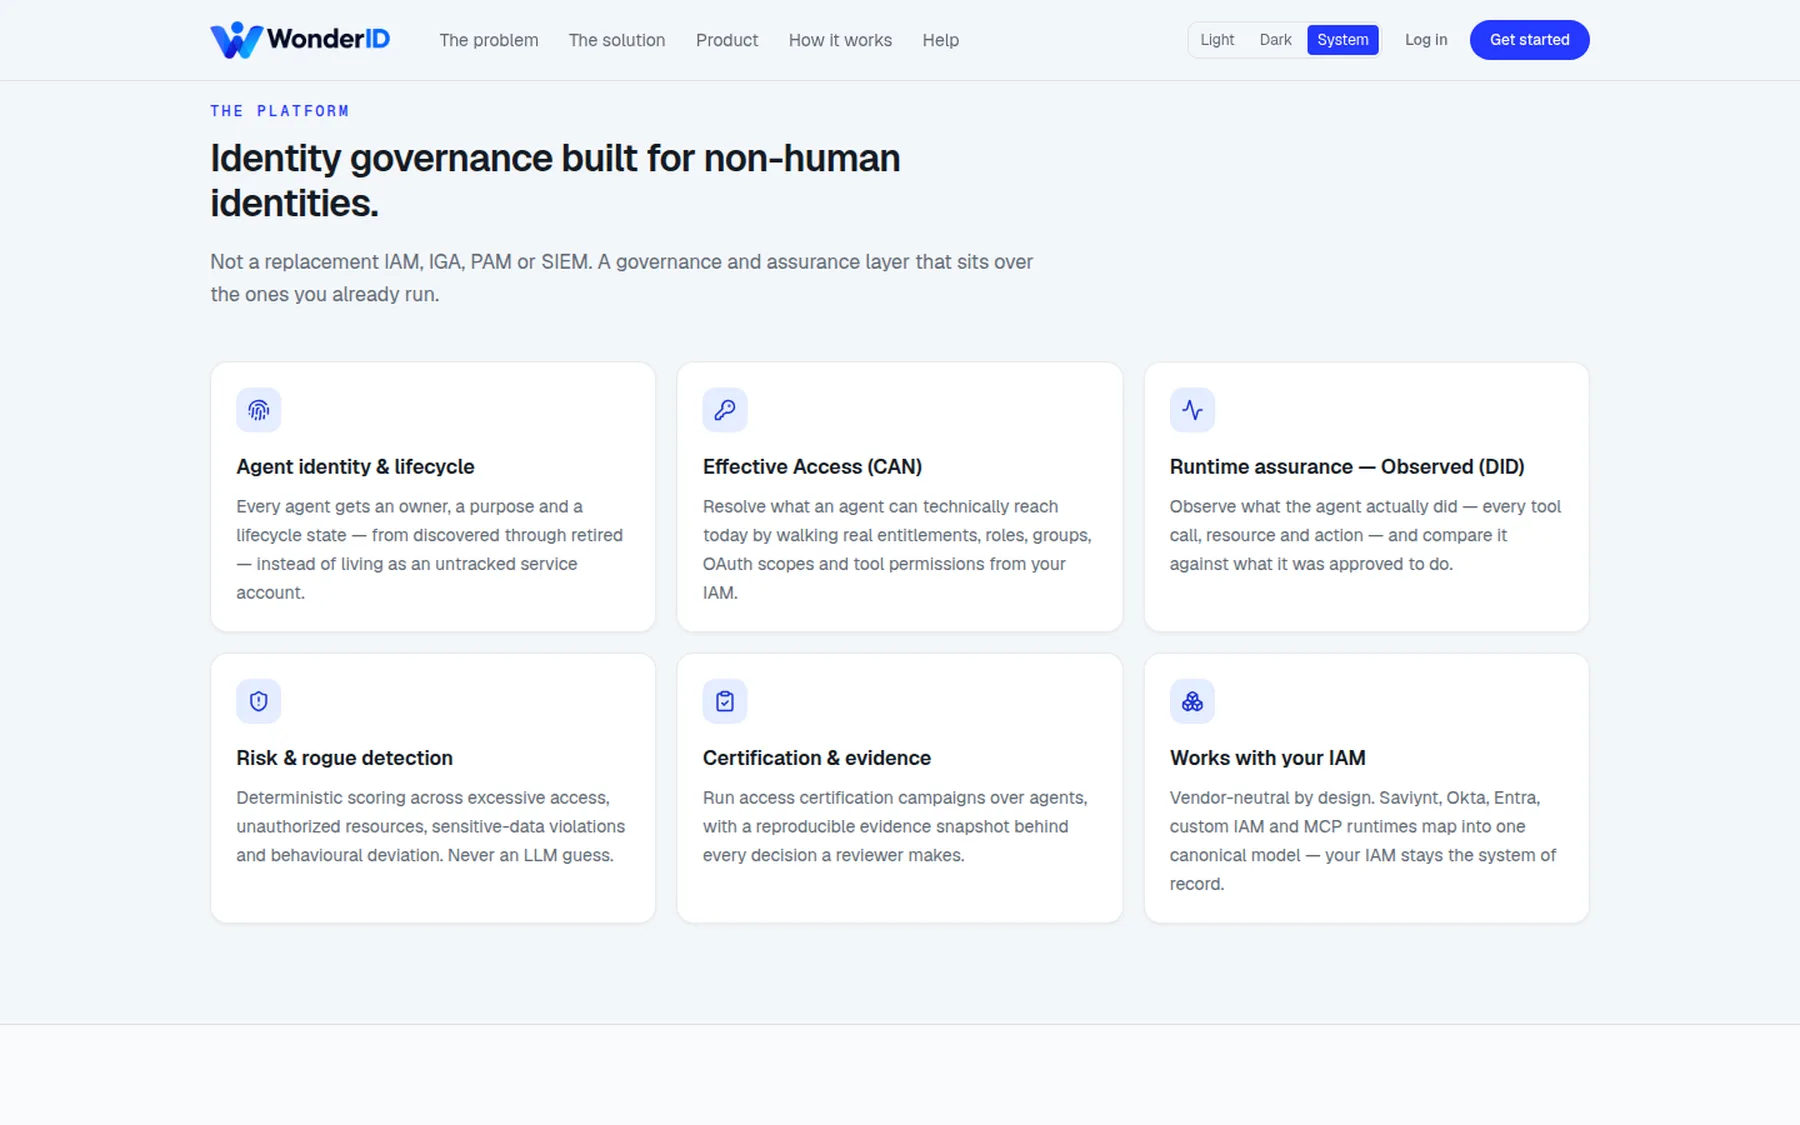
A governance layer over the IAM you already run
The WonderID brand, rolled out across every surface
Market & why now
Every identity is an attack surface — and most of them aren't people.
Enterprise IAM was built for employees. Service accounts, workloads and APIs already sprawl beyond them, and AI agents add autonomy on top. Security leaders need one answer to 'who and what has access, who owns it, why, and what did they do with it?' — and proof for auditors.
Who buys
- Regulated enterprises in finance, healthcare and public sector
- Organisations rolling out MCP-based agent platforms
- IAM/IGA teams consolidating human, machine and agent identity governance
- GRC teams facing AI-specific audit requirements
Why now · 1
Agent adoption is outpacing governance; MCP has standardised how agents reach tools, which makes runtime observation tractable.
Why now · 2
Regulators and auditors are asking for demonstrable control over AI systems, not policy documents.
Why now · 3
Incumbent IGA suites are strong on human identity and bolt agents on; a vendor-neutral layer that starts from the agent and keeps existing IAM as system of record is the low-friction path in.
Business model
Enterprise SaaS, priced per tenant.
Multi-tenant from day one with a separate vendor-only platform-admin boundary for tenants, subscriptions, feature flags, usage and health. Deployment-ready today; commercial packaging follows the first design customers.
Pilot
Read-only proof
- Connect one IAM and one runtime source
- Discover and register agents
- First risk findings and a certification round
Enterprise
Governance in production
- Unlimited identities and integrations
- Identity directory, application onboarding and self-service access
- SSO/MFA, scoped roles and permissions
- Certification, evidence packs and human-confirmed remediation
Defensibility
What compounds.
Agent-first, identity-wide
Incumbent suites bolt agents onto a human model. WonderID started from the agent — owner, purpose, effective access, observed behaviour — and extends outward, so an AI agent is a first-class identity rather than a column on a service-account table.
Deterministic by architecture
No authorisation, risk, policy or remediation decision depends on a language model. AI writes advisory summaries and proposals only. That is an auditable promise competitors chasing 'AI security' cannot easily make.
Vendor-neutral canonical model
Saviynt, SailPoint, Entra, Okta, custom IAM and MCP map into one model without any becoming the internal architecture.
Built to enterprise bar from line one
Tenant RLS on every table, server-side tenant context, immutable audit, encrypted credentials, CSP headers, rate-limited auth — verified by a dedicated QA module.
Execution to date
Verifiable, not aspirational.
Pulled from the product's own public engineering trackers. Source code, trackers and live demos are available to serious parties on request.
Stories complete
187 / 239
78% across 11 modules; the tracker grew by 74 stories when WonderID's identity roadmap was adopted
WonderID roadmap
14 of 36 done
Identity directory, reconciliation, application onboarding, account inventory, requests, approvals and access packages shipped; 4 more partial
API surface
168 routes
143 call requirePermission directly; 100 database migrations
Screens
78 + 8
Customer pages plus the vendor platform-admin console
Roadmap
What comes next.
Now
- Business and IT roles, preventive SoD and delegations
- Provisioning and deprovisioning pipeline
- Access ledger, imported-access classification and Rogue Access management
Next
- Certification campaigns for every identity type
- Passkey (WebAuthn) sign-in and step-up
- WonderID Home and a My Access self-service portal
Later
- Configuration Studio and a workflow designer
- An advisory-only WonderID AI assistant
- Partner and MSSP editions
The ask